Offensive security
Penetration testing, red teaming and threat-led testing that show how an attacker would reach what matters.
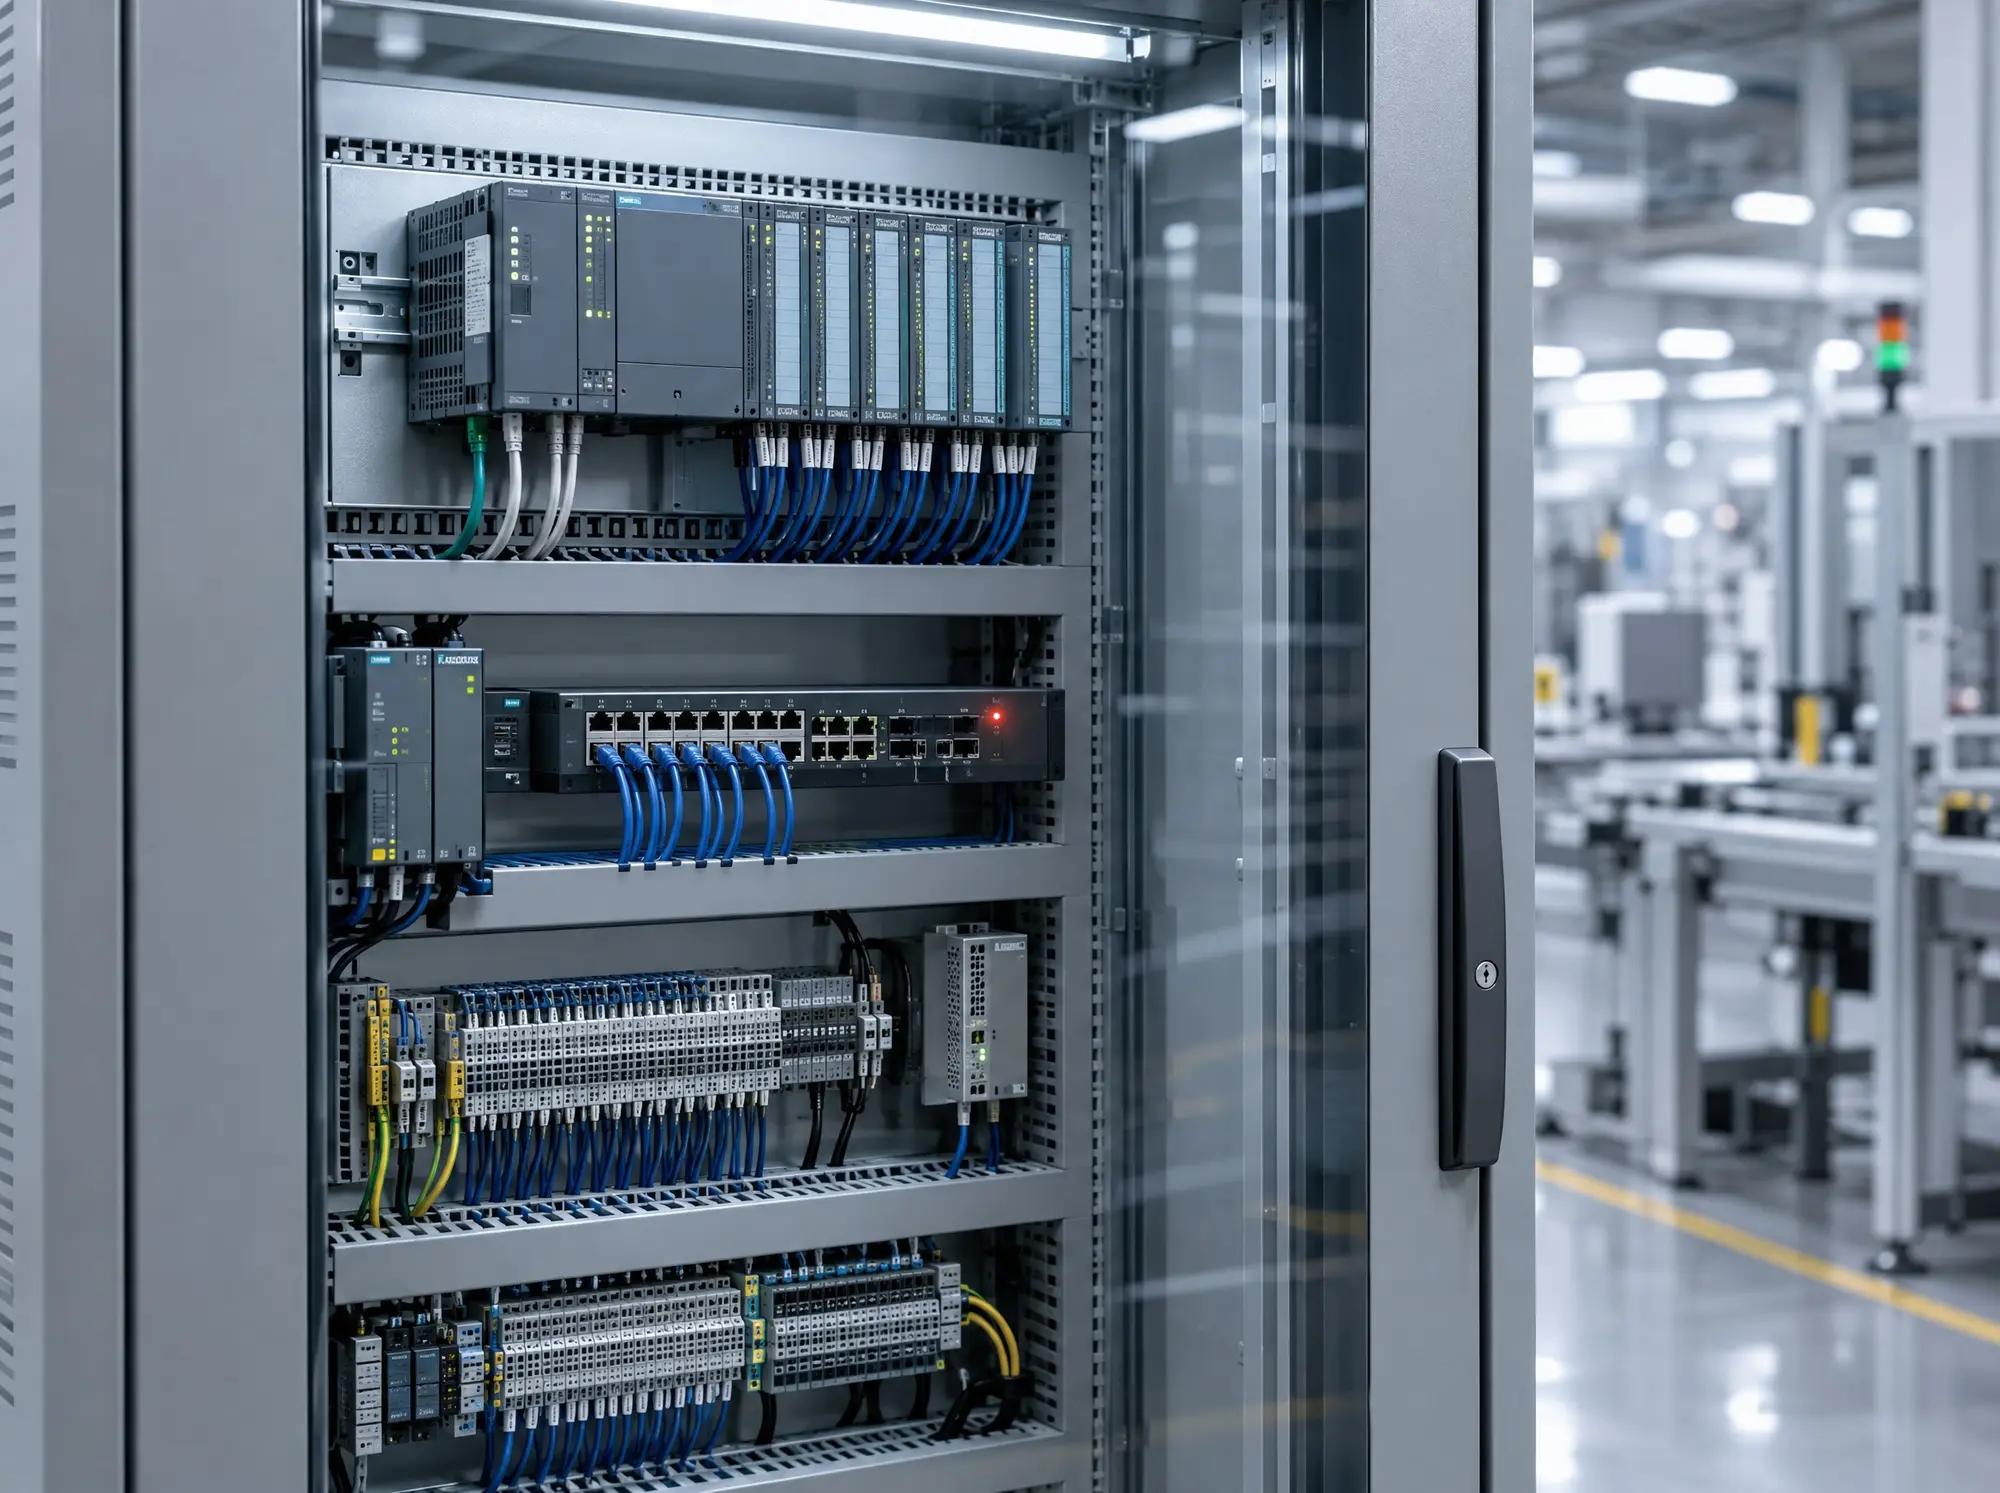
We test web applications, internal networks, cloud tenants, mobile apps and industrial environments. Each test is scoped around a question the client needs answered, such as whether a supplier connection can reach the production network, rather than a fixed number of days. Reports describe the attack path, the evidence and the fix, written for both engineers and management.
For financial entities we support threat-led penetration testing under DORA and red team exercises aligned with TIBER-EU and its national implementations such as TIBER-DE. In Switzerland we run comparable scenario-based red team exercises for banks and insurers, using the same principles of threat intelligence, controlled execution and joint learning with the defending team.
Typical deliverables
- Penetration test report with attack paths, evidence and remediation guidance
- Red team scenarios based on threat intelligence for the client's sector
- Purple team workshops to turn findings into detection rules
- Retest and closure confirmation for remediated findings
Talk to us about your security priorities
Tell us about your organisation, the regulations that apply to you and what you need to achieve, and we will come back to you to arrange a confidential first call. Email contact@alpwacht.com. If you are dealing with an active incident, say so in the subject line.
contact@alpwacht.com